

Appearance
Cisco Meraki Integration
Connect CaptiFi to your Cisco Meraki wireless network using Meraki's click-through splash page. This is the simplest integration of all: no API keys, no controller credentials, no RADIUS.
Quick setup
Most venues complete this in under 15 minutes. You only need your Meraki Dashboard login and the sign-in address CaptiFi gives you for the venue.
Prerequisites
- Cisco Meraki MR access point(s) online in your Meraki Dashboard
- Dashboard admin access for your organisation/network
- CaptiFi account at my.captifi.io
How it works
- A guest connects to your guest SSID
- Meraki redirects them to your CaptiFi splash page (passing a one-time grant URL)
- The guest completes the splash form
- CaptiFi sends the guest's browser back to Meraki's grant URL, and Meraki authorises the session automatically
- Meraki sends the guest on to your venue's redirect page
No server-to-server API calls are involved. It's all handled in the guest's browser.
Add the venue in CaptiFi
The custom splash URL and the walled garden list both come from the venue in CaptiFi, so add the venue before you open the Meraki Dashboard.
- Log in to my.captifi.io, go to My Venues and click Add venue at the top right
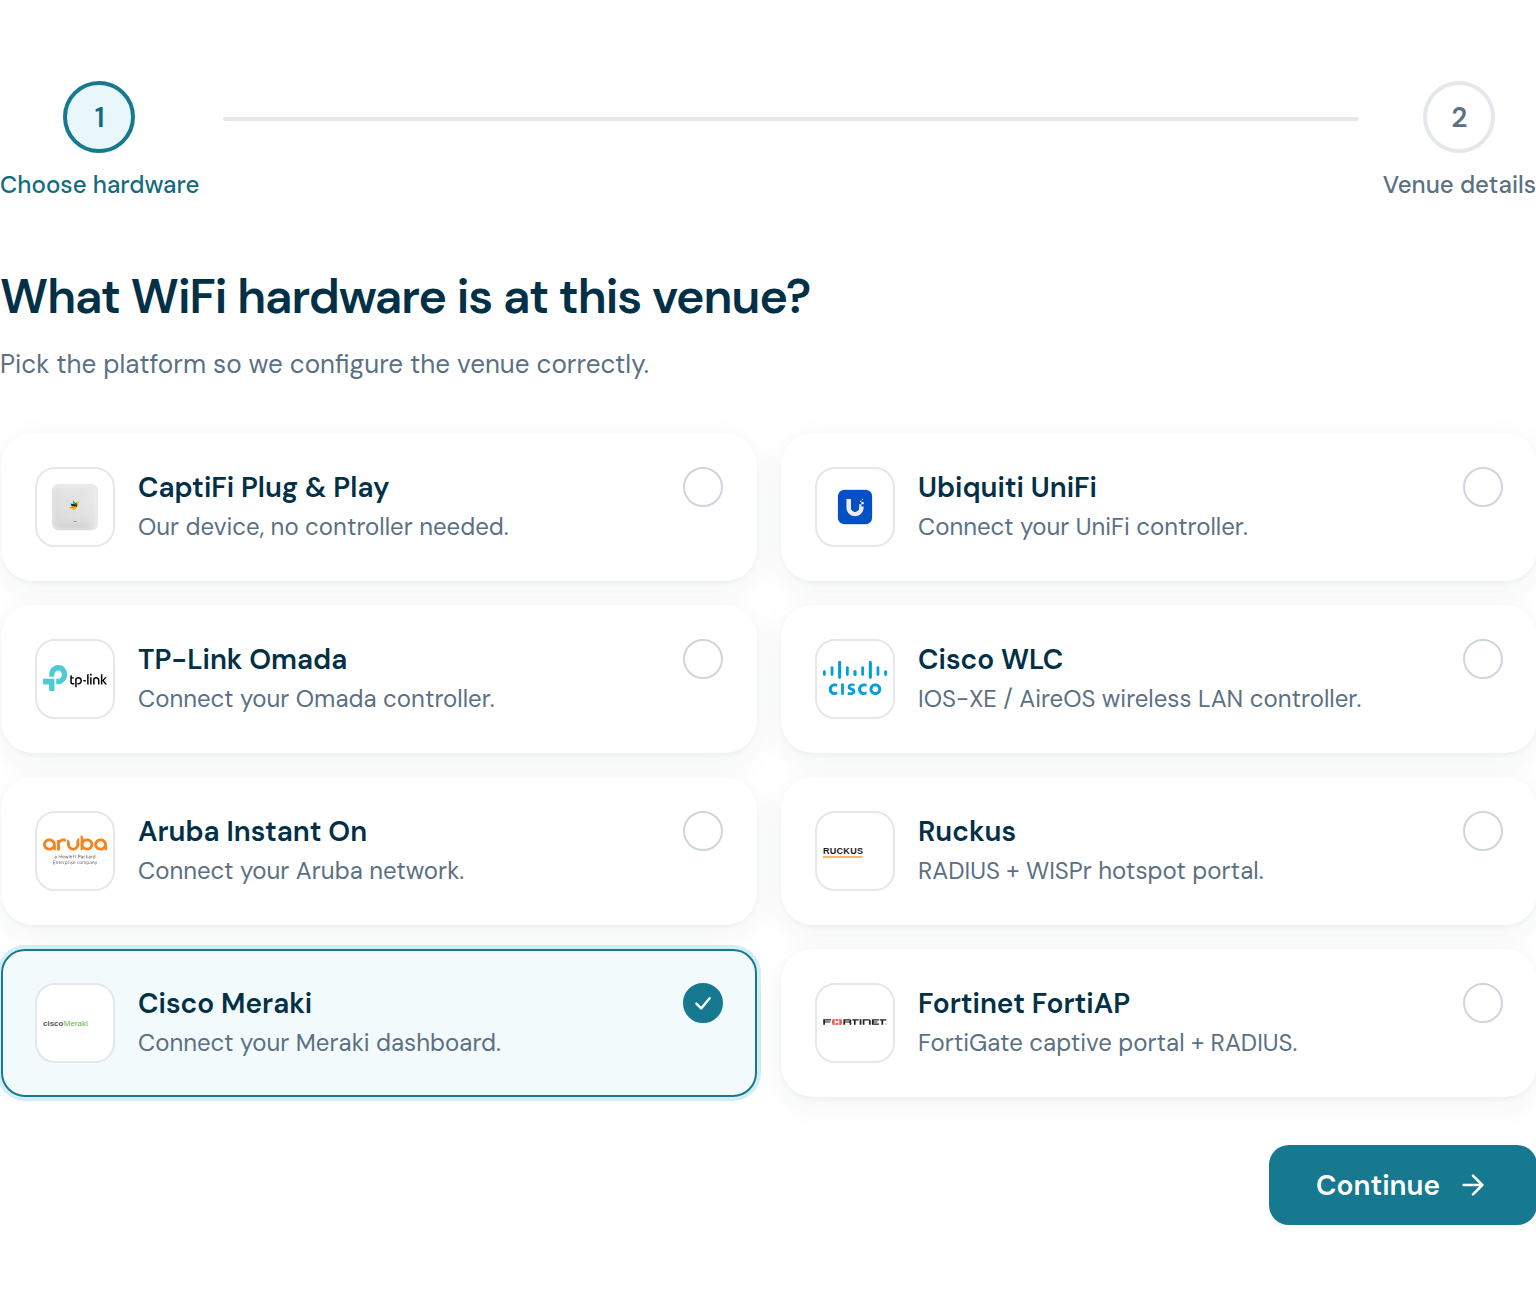
- On What WiFi hardware is at this venue?, choose Cisco Meraki and click Continue
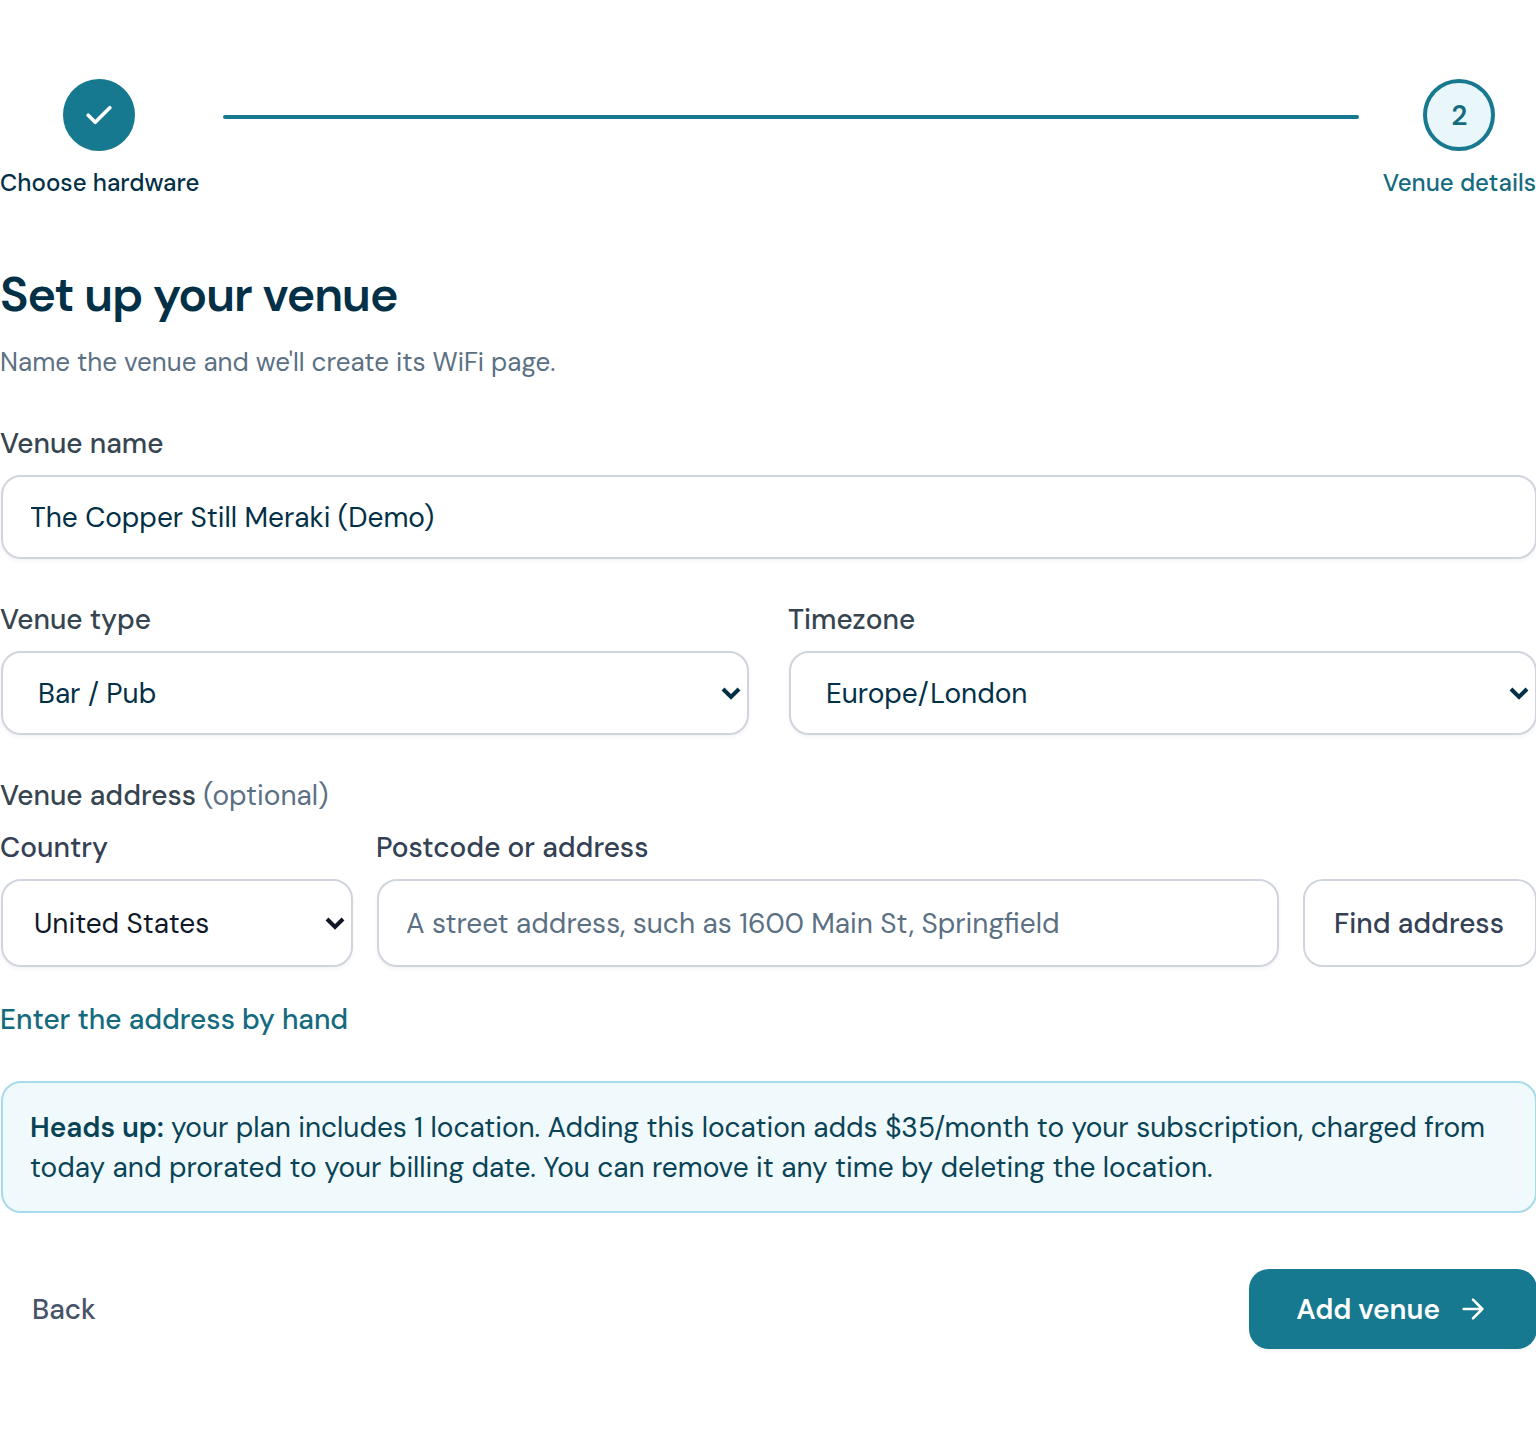
- On Set up your venue, enter the Venue name, set the Venue type and check the Timezone. Venue address is optional. Click Add venue
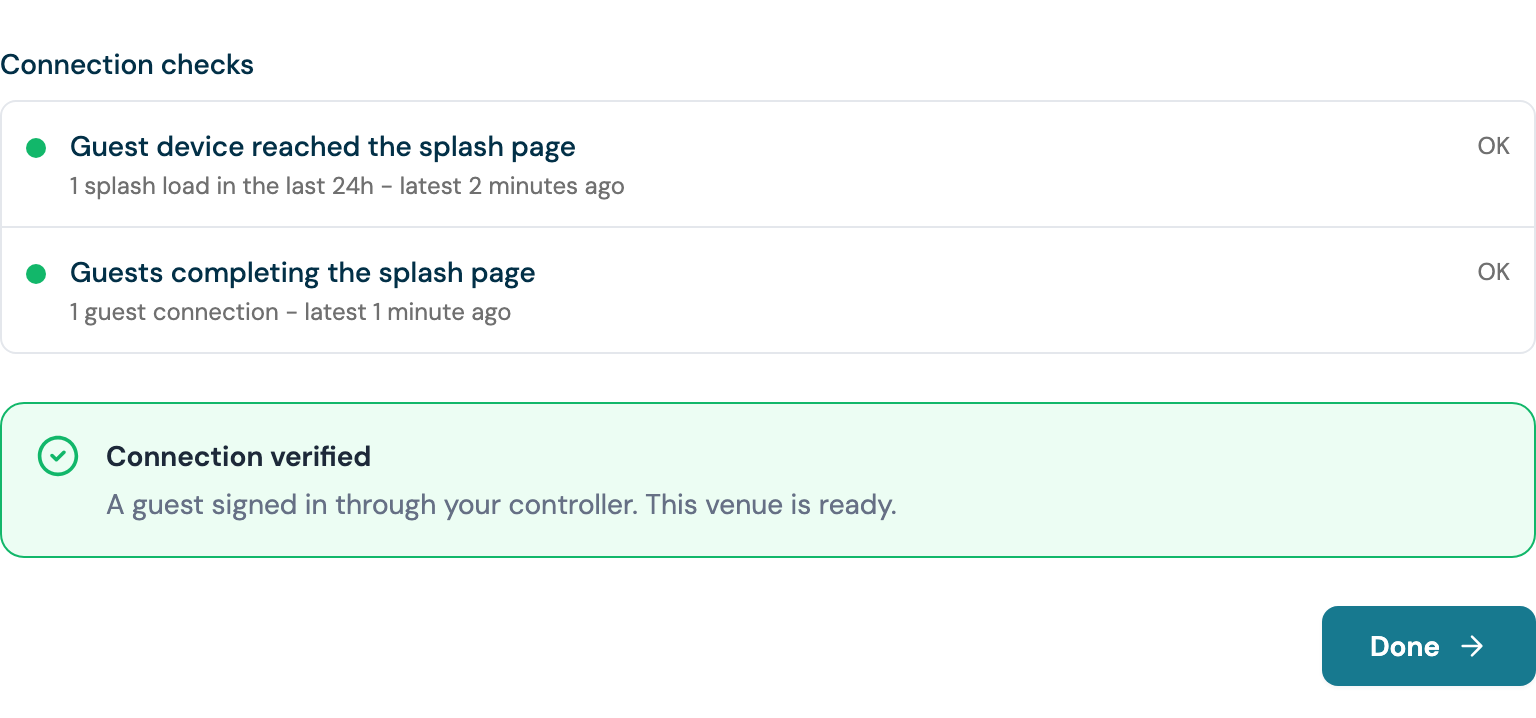
- The Set up your controller page opens. Copy the Guest sign-in address, which is the custom splash URL for Meraki with your site ID already in it, then copy the Allowed domains (walled garden) list. Leave the page open: the Connection checks further down it tick off when your first guest connects, and Done unlocks once they have
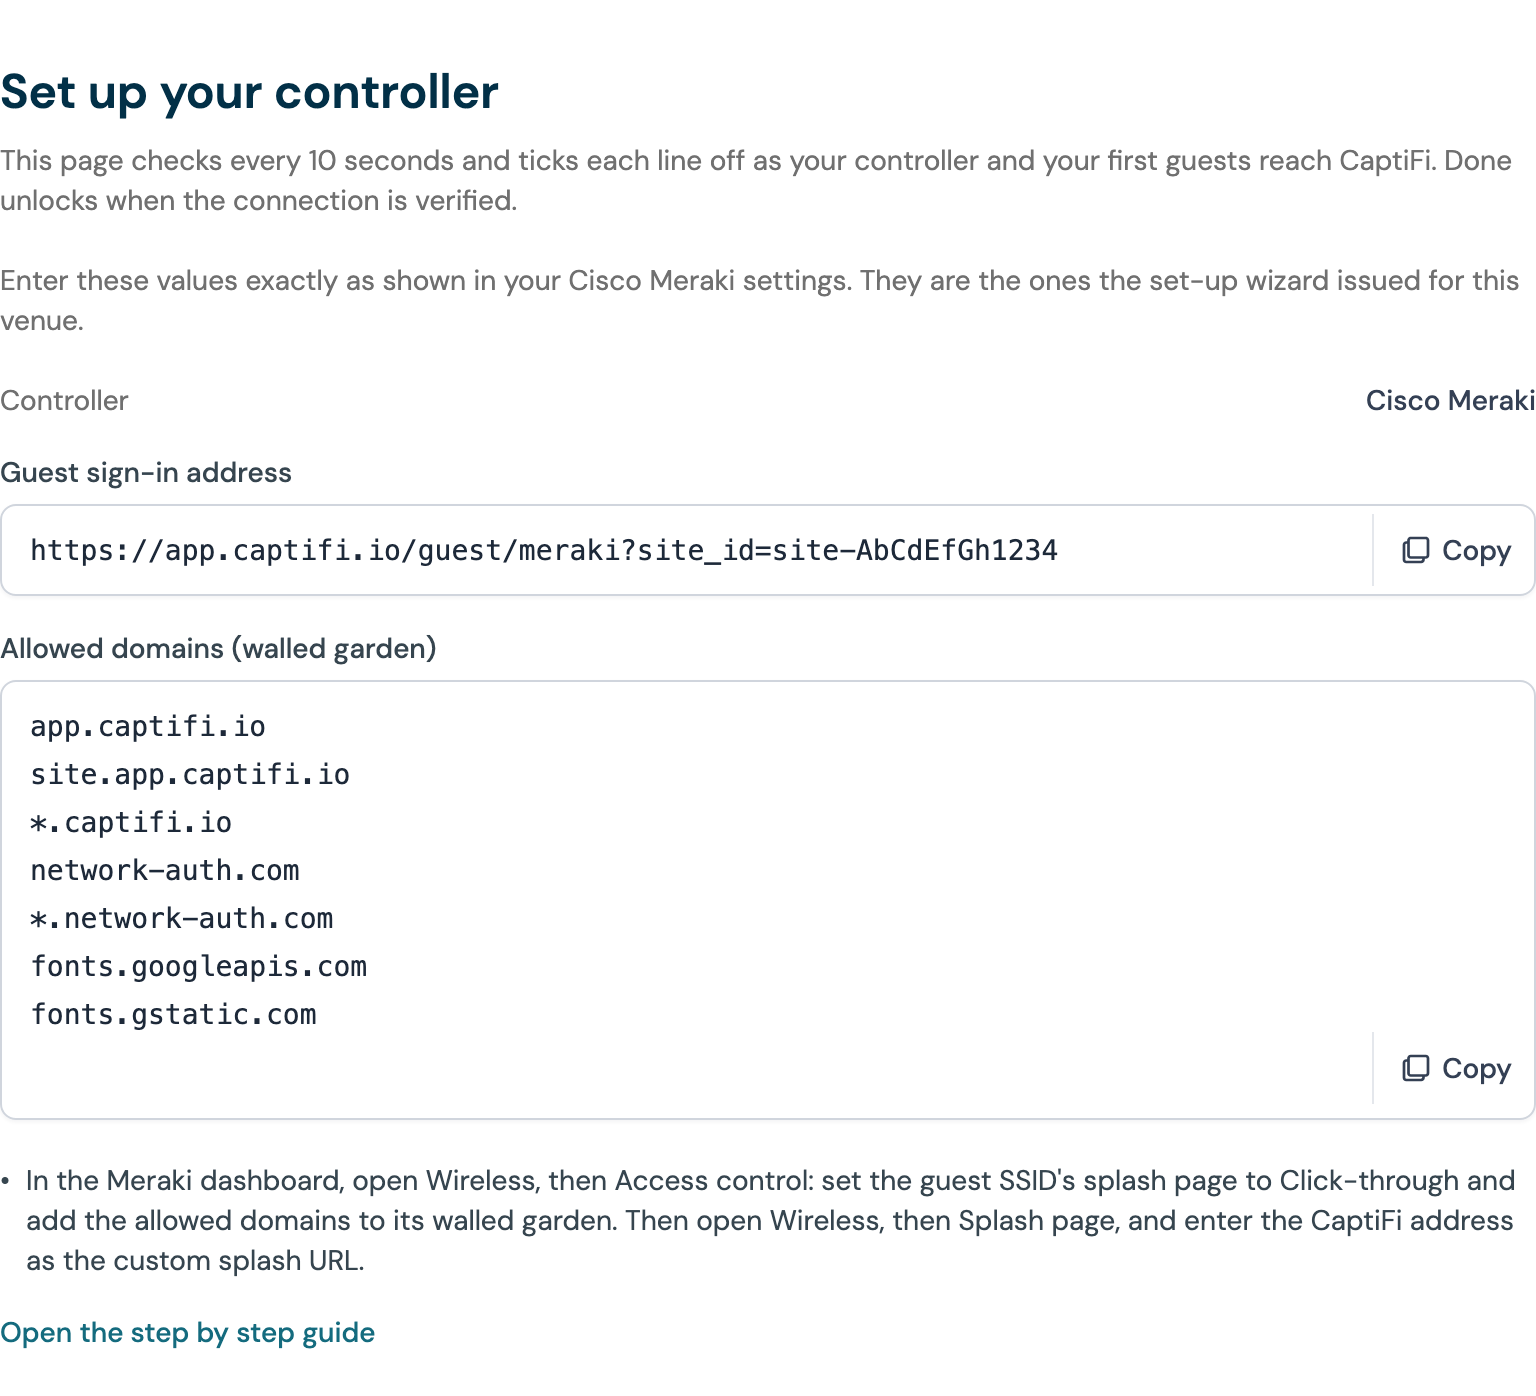
If you close the page, Resume setup on the venue card opens it again. Once set-up is finished, the same values are on the venue's Connection page: More, then Connection on its card, under Controller settings.
On a new account, choose Cisco Meraki in the set-up wizard. Its Configure your controller step shows the same address and list with copy buttons.
Step 1: Turn on the click-through splash page
- In the Meraki Dashboard, go to Wireless → Configure → Access control
- Choose your guest network in the SSID dropdown at the top
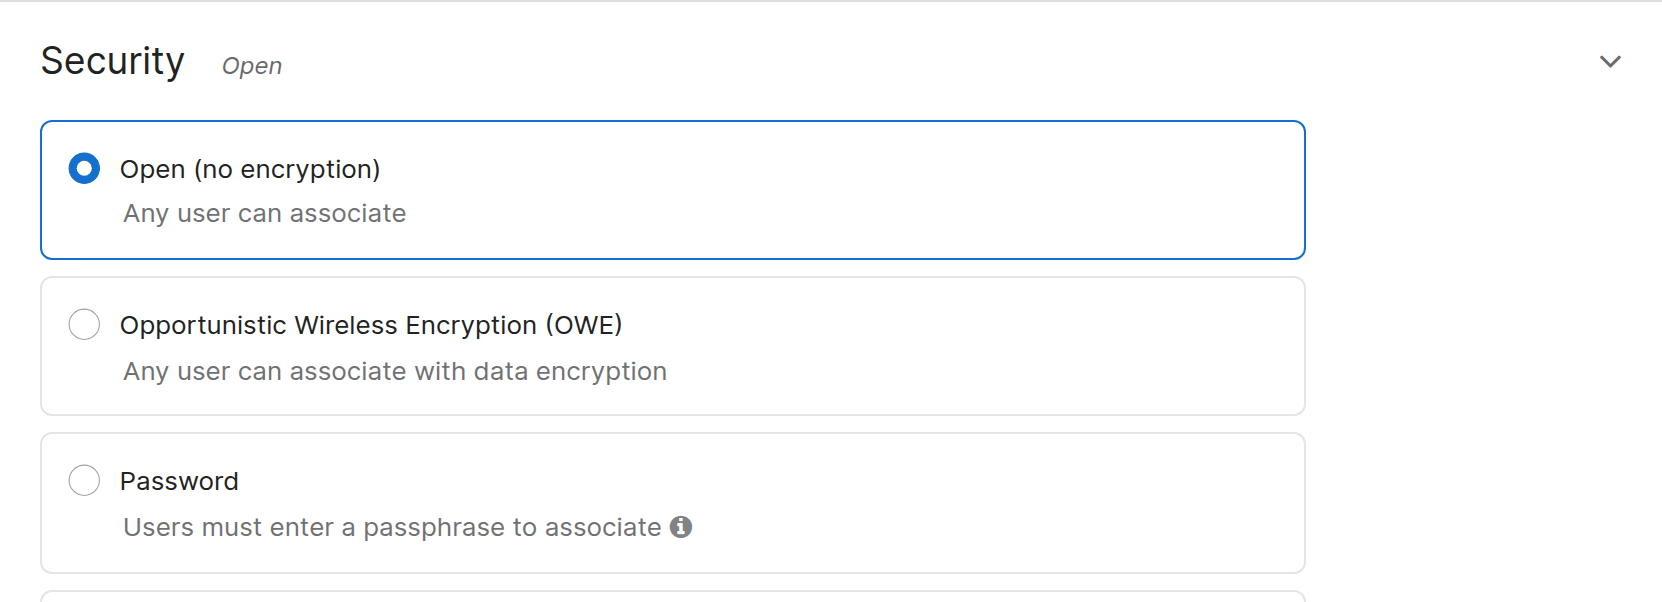
- Under Security, choose Open (no encryption)
- Under Splash page, choose Click-through
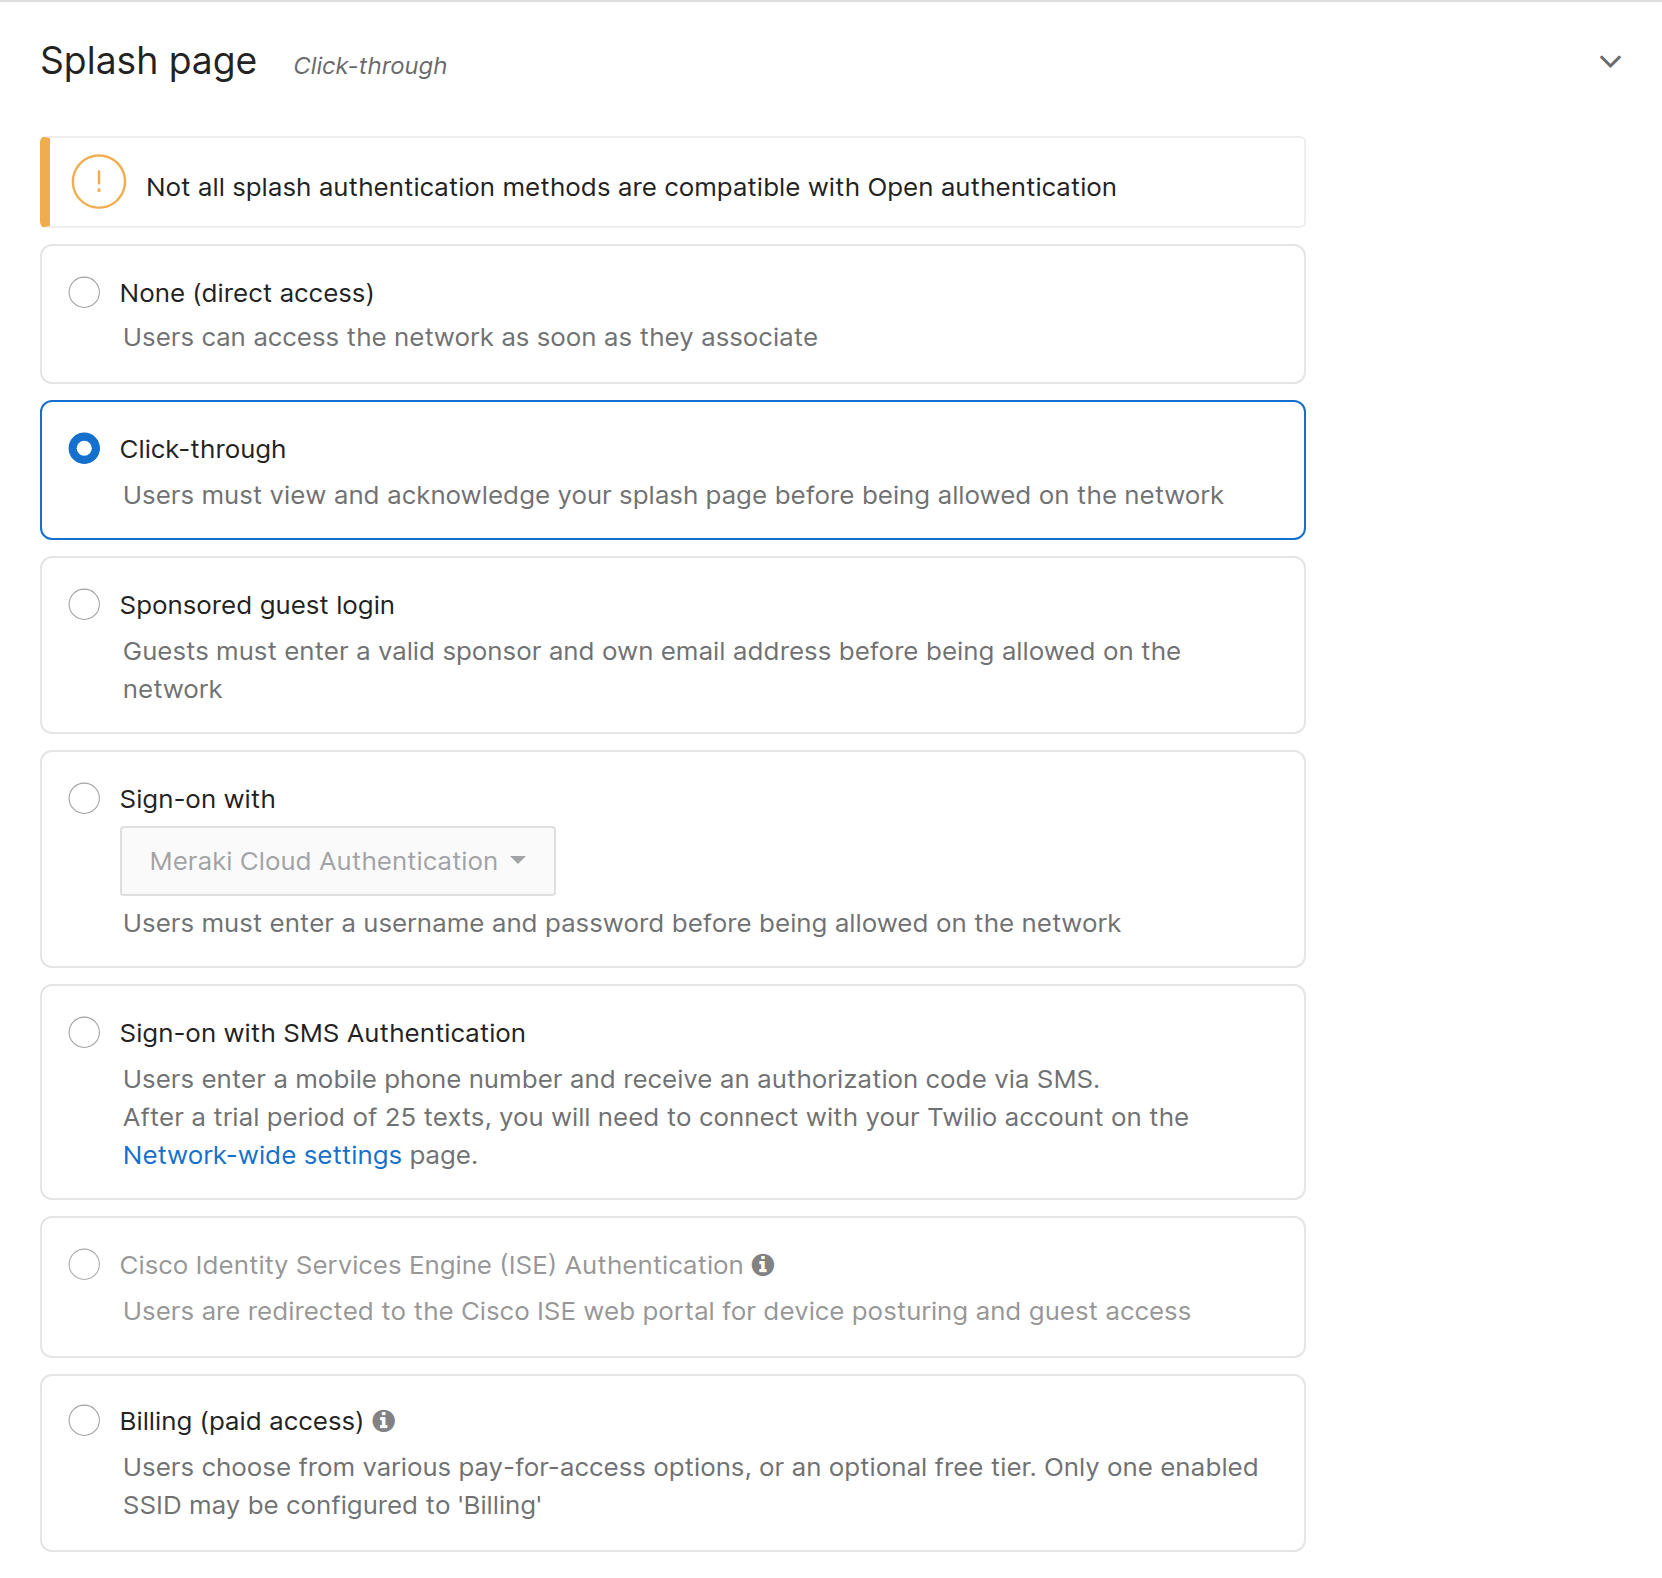
Stay on this page for the next step.
Two versions of this page
These steps follow the current version of Meraki's Access control page. If your dashboard opens the older version, the banner at the top of the page links to the new one.
Step 2: Add the walled garden domains
The walled garden lets guests reach CaptiFi's servers before they are signed in. Without it, the splash page cannot load.
- Under the splash page options, open Advanced splash settings
- Leave Captive portal strength on Block all access until sign-on is complete
- Set Walled garden to Enabled
- Paste the Allowed domains (walled garden) list you copied from CaptiFi into Walled garden ranges, one entry per line:
app.captifi.io
site.app.captifi.io
*.captifi.io
network-auth.com
*.network-auth.com
fonts.googleapis.com
fonts.gstatic.com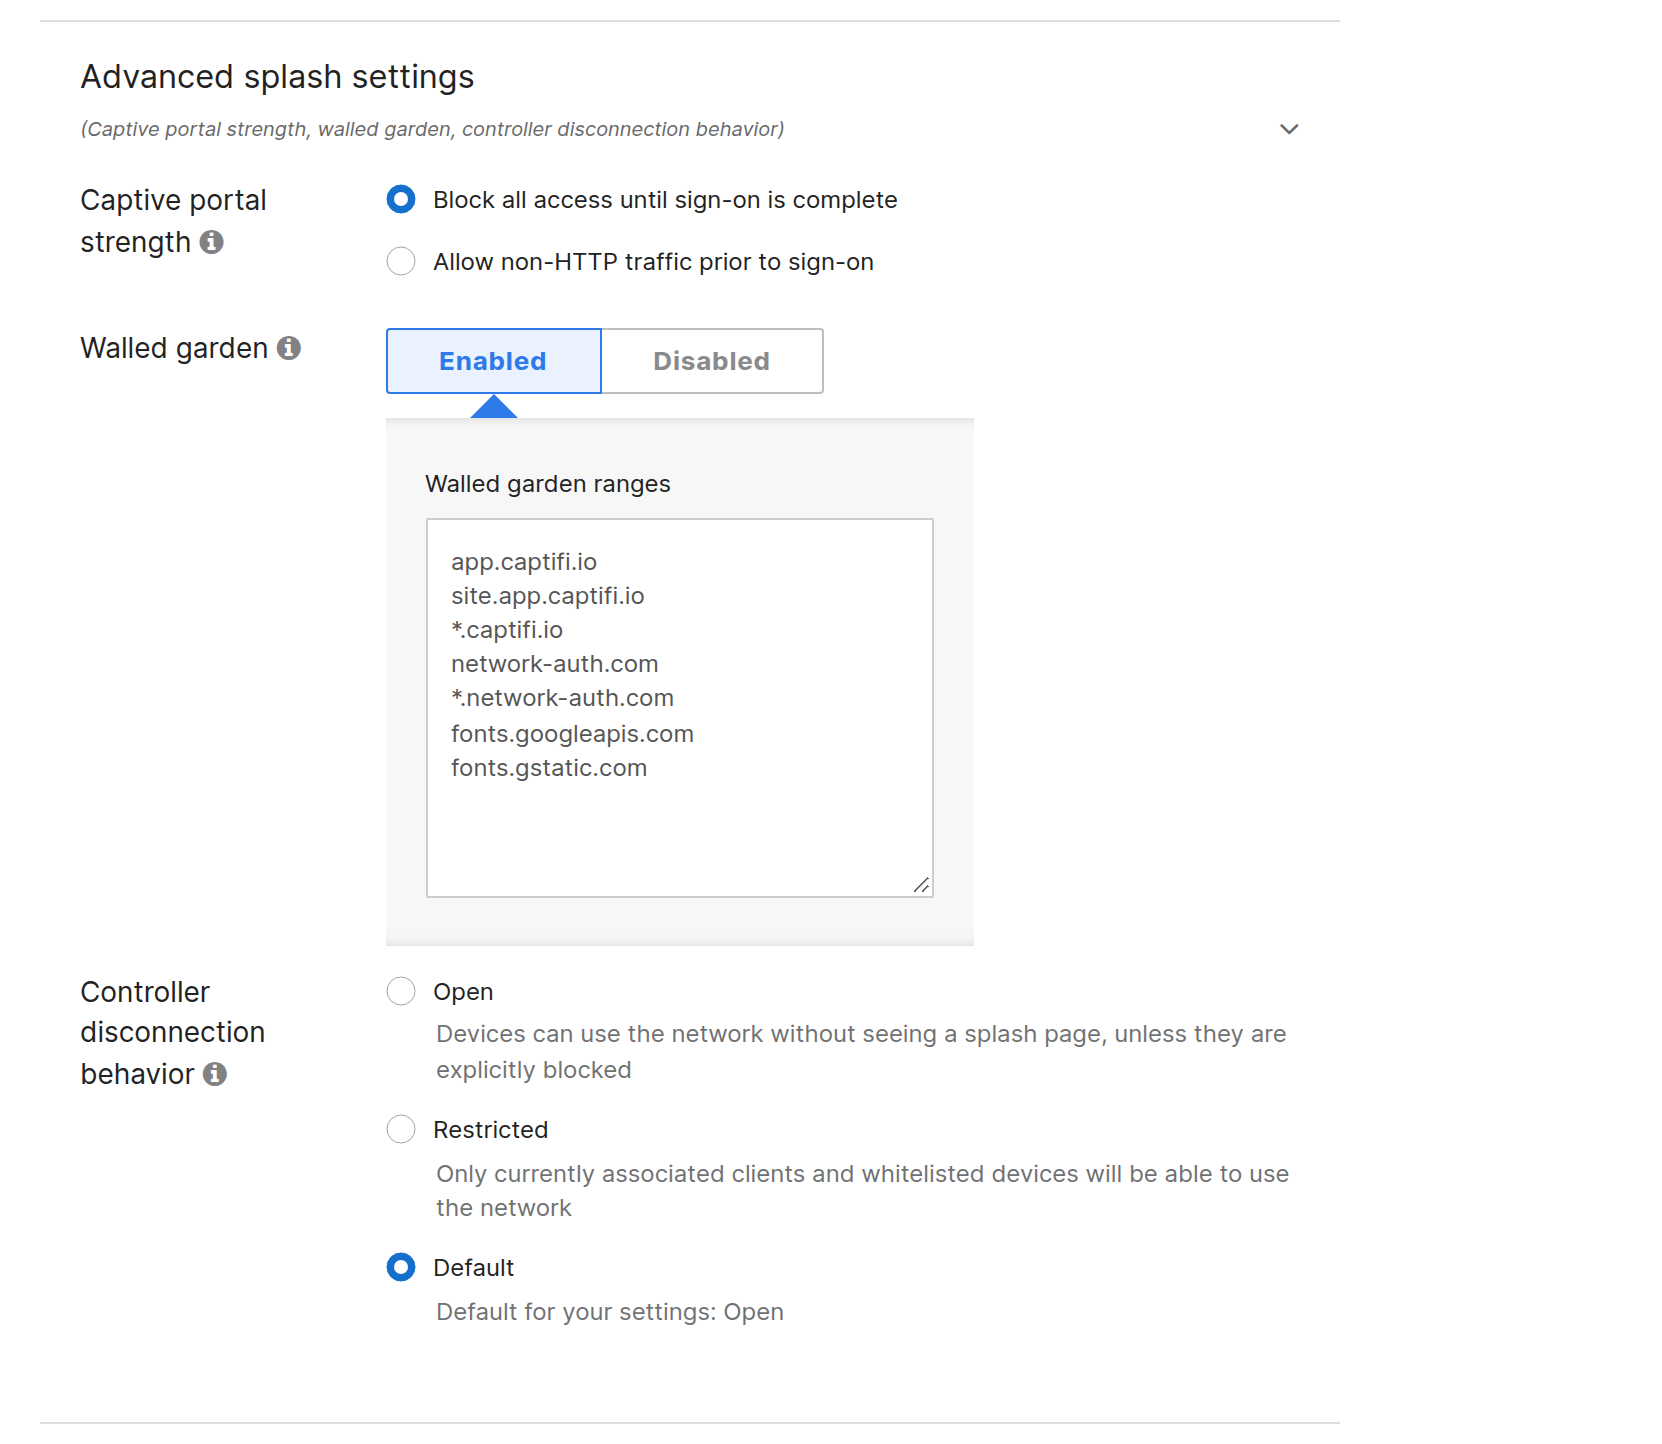
- Click Save at the bottom of the page
Don't skip the network-auth.com entries
network-auth.com and *.network-auth.com are Meraki's own authorisation hosts. Without them, guests can complete your splash page but Meraki never grants them access.
Step 3: Set the custom splash URL
- Go to Wireless → Configure → Splash page and choose your guest network in the SSID dropdown. The page should say that splash pages on this SSID are enabled because a click-through splash page is enabled. If it does not, go back to Step 1
- Under Custom splash URL, select Or provide a URL where users will be redirected: and paste the Guest sign-in address you copied from CaptiFi. It looks like this, with your own site ID at the end:
https://app.captifi.io/guest/meraki?site_id=YOUR_SITE_ID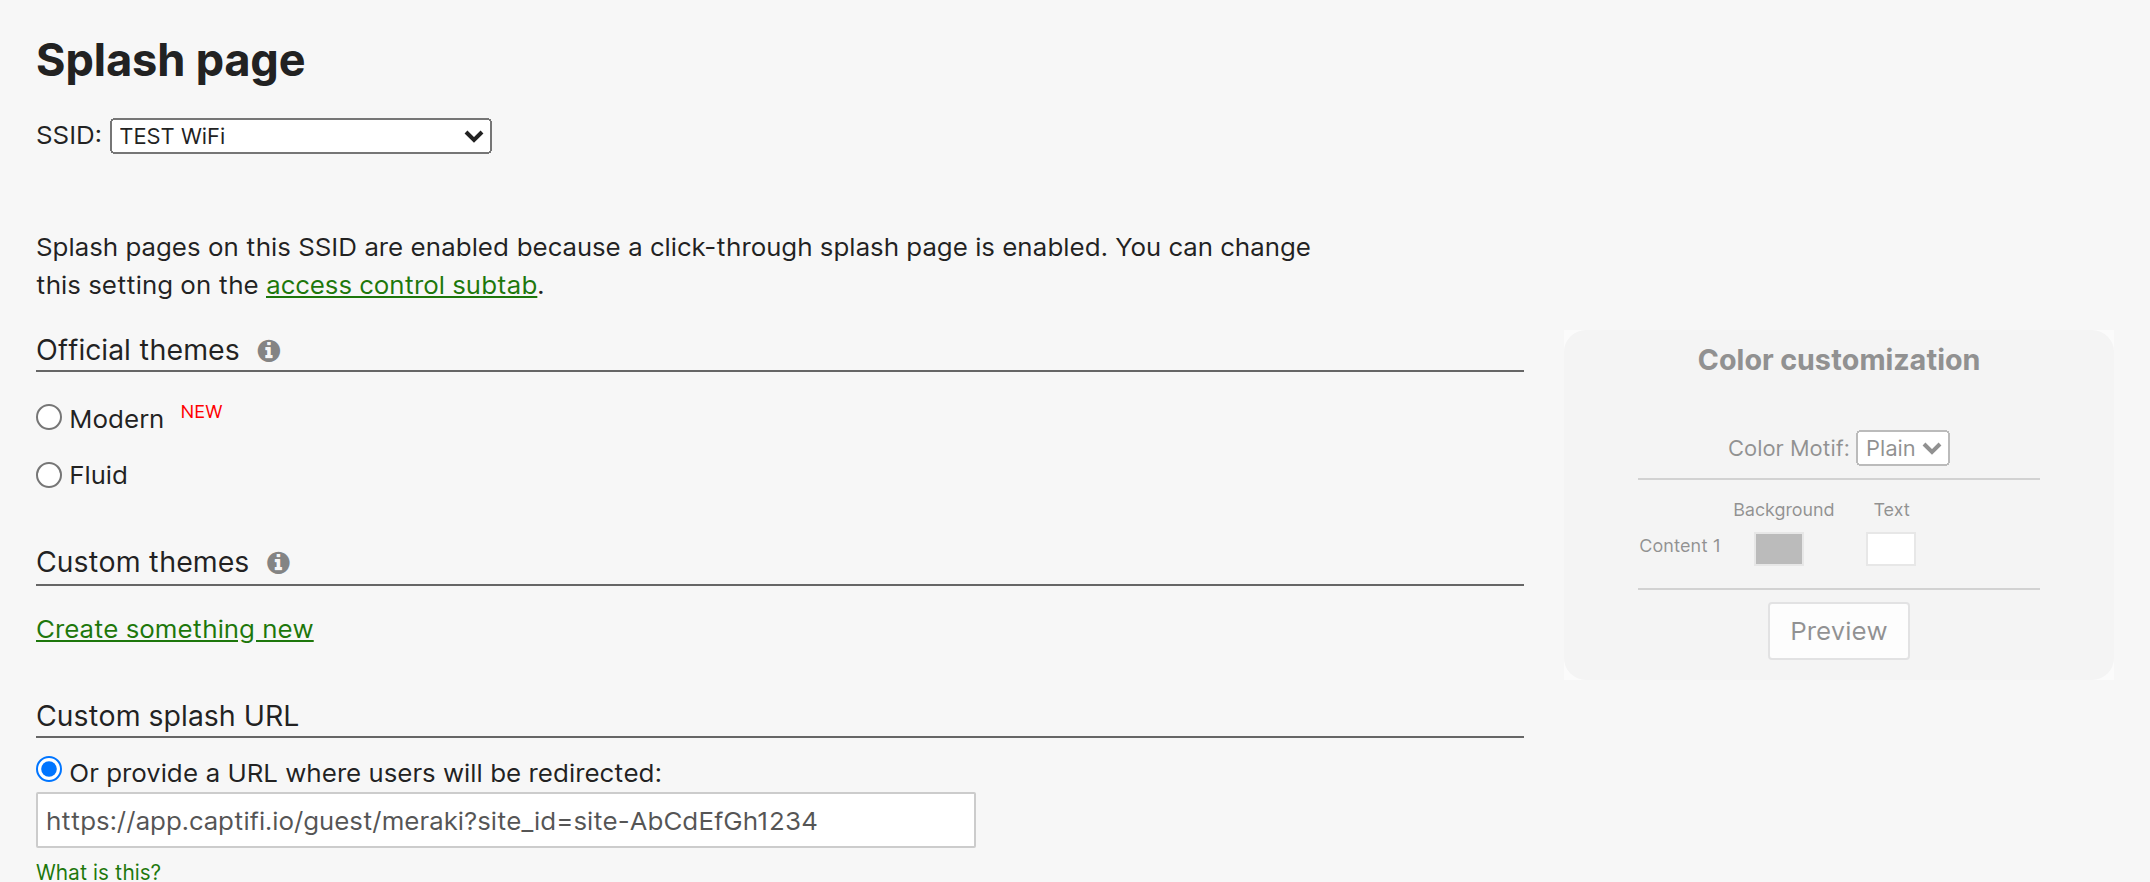
- Under Splash behavior, leave Where should users go after the splash page? on The URL they were trying to fetch. CaptiFi tells Meraki to send each guest on to your venue's redirect page once they have signed in, and Meraki only does that with this option selected. Set Splash frequency to how often returning guests should see the splash page
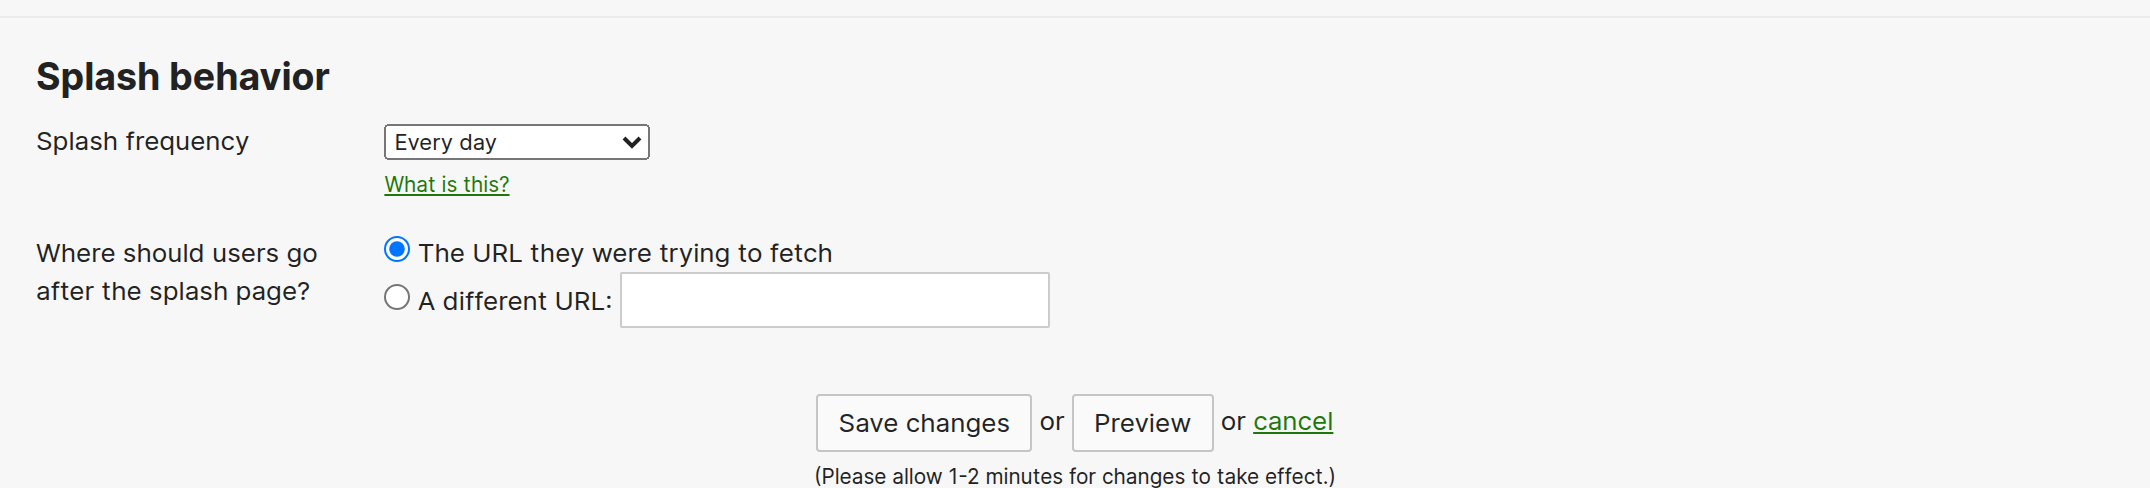
- Click Save changes
Step 4: Test
- Wait 1 to 2 minutes for the configuration to push to your access points
- Connect a phone to your guest SSID
- The CaptiFi splash page should appear automatically
- Complete the form. You should be granted access and redirected
- Check your CaptiFi dashboard: the guest appears under Guests, and the two Connection checks on the Set up your controller page tick off as the phone reaches the splash page and signs in. In the set-up wizard the same checks are on the Check the connection step. Once both are OK, Connection verified shows under them and Done unlocks (Finish setup in the wizard)
Troubleshooting
| Issue | Solution |
|---|---|
| Splash page not appearing | Verify Splash page is set to Click-through and the custom splash URL is saved on the correct SSID |
| Blank or broken splash page | Check all seven walled garden entries are present. fonts.googleapis.com and fonts.gstatic.com are needed for page assets |
| Guest completes form but is never authorised | Add network-auth.com and *.network-auth.com to the walled garden. The grant redirect goes through Meraki's own domain |
| "Back in a moment" for about two minutes, then a "WiFi sign-in isn't set up yet" page, instead of the splash | The site_id in your splash URL is missing or wrong. Copy it again from your CaptiFi dashboard. On a shared splash URL with no site_id, add the access point under WiFi Access Points (see One splash URL for several venues) |
| Guest completes form but no internet | Ensure Captive portal strength is "Block all access until sign-on is complete" and the SSID firewall isn't blocking post-auth traffic |
| Guest gets online but sees a plain "Success" page, not your redirect page | On Wireless → Configure → Splash page, set Where should users go after the splash page? to The URL they were trying to fetch. With A different URL selected, Meraki sends guests to that address |
| Works on some APs only | Confirm all MR access points are online and broadcasting the guest SSID; configs can take a couple of minutes to push |
| HTTPS sites not triggering redirect | Guests may need to visit an HTTP site first (e.g. http://example.com) to trigger the portal |
One splash URL for several venues
If one Meraki network or SSID configuration serves several CaptiFi venues, you can use https://app.captifi.io/guest/meraki as the custom splash URL, with no site_id. Meraki adds each access point's MAC address to the redirect as node_mac, and CaptiFi sends the guest to the venue you added that access point to under WiFi Access Points, Add access point. Add every access point first: a guest whose access point is not added sees "Back in a moment" for about two minutes, then a "WiFi sign-in isn't set up yet" page. Everything else in this guide stays the same. See One Portal Address for Several Venues.
Session length
With click-through splash, the session duration is controlled by Meraki's Splash frequency setting (Wireless → Configure → Splash page, under Splash behavior). Set it to how often you'd like returning guests to see the splash page (e.g. every day, every week).
Next steps
Need help?
- Email: support@captifi.io
- Live Chat: Available on captifi.io
- Meraki Documentation: Splash Page Overview